Description
Smart Contract Fraud Investigation
A smart contract fraud investigation examines suspicious smart contracts, wallet approvals, blockchain transactions, and cryptocurrency movements associated with suspected fraud.
Smart contracts are programs deployed on blockchain networks. They can perform actions according to their programmed logic, including transferring tokens when the appropriate permissions have been granted.
That functionality can also be abused.
A victim may believe they are connecting to a legitimate decentralized application, claiming an airdrop, purchasing a token, participating in a presale, or completing another routine Web3 action when the transaction actually grants dangerous permissions or transfers assets.
Ethereum’s official security guidance warns that malicious contracts can contain backdoors or request excessive token permissions.
A smart contract fraud investigation therefore looks beyond the website or message that initially attracted the victim. The investigation examines what the contract actually did, what permissions were granted, what transactions followed, and where the assets subsequently moved.
The investigation may include:
- Smart contract address analysis
- Transaction analysis
- Token approval analysis
- Wallet activity analysis
- Fund-flow reconstruction
- Contract interaction analysis
- Potential exchange destination identification
- Cross-wallet tracing
- Cross-chain analysis where applicable
- Evidence organization
- Forensic reporting
The objective is to establish a factual transaction trail that can help the victim, attorney, investigator, business, or law-enforcement agency understand the incident.
What Is Smart Contract Fraud?
Smart contract fraud occurs when blockchain-based functionality is used as part of a deceptive or unauthorized scheme.
The fraudulent activity may involve a malicious contract, deceptive website, fake decentralized application, fake token, fraudulent presale, phishing campaign, or manipulated transaction approval.
One particularly important form is approval phishing.
A token approval gives a smart contract or address permission to spend specified tokens on behalf of a wallet. Revoke.cash explains that token approvals are commonly used by decentralized exchanges, lending protocols, and other applications, but the same mechanism can create security risks when granted to malicious actors.
Chainalysis describes approval phishing as a tactic in which a victim is tricked into signing a transaction that gives an attacker permission to spend tokens held by the victim’s wallet.
This is why a smart contract fraud investigation may need to examine both the contract and the wallet’s subsequent transactions.
Common Types of Smart Contract Fraud
1. Approval Phishing
Approval phishing occurs when a victim is tricked into authorizing token spending by an address or contract controlled by a malicious actor.
The transaction may appear harmless to the victim while granting a significant spending allowance.
Chainalysis has documented approval-phishing schemes in which the approved spender subsequently transfers assets from victims’ addresses.
A smart contract fraud investigation can examine:
- The approval transaction
- The approved spender
- The token involved
- The amount or allowance
- Subsequent transfers
- Receiving addresses
- Related wallet activity
2. Drainer Contracts
A drainer-related scam may use deceptive signing requests or permissions to facilitate unauthorized transfers.
The investigation can examine the transaction sequence to determine whether the victim authorized an approval and whether another address subsequently used that permission.
Our Wallet Drainer Recovery service may be relevant when the incident involves a wallet-draining scheme.
3. Fake Presale Contracts
A fake presale may advertise a cryptocurrency project that does not operate as represented.
Victims may be instructed to send ETH, USDT, or another asset to a contract or wallet.
A smart contract fraud investigation can examine whether the contract contains the expected token-distribution or presale functionality and where the deposited assets subsequently moved.
4. Malicious Airdrop Claims
Fake airdrops can encourage users to visit a website and sign a transaction.
The transaction may grant permissions or interact with a malicious contract rather than simply claiming tokens.
5. Honeypot Tokens
A honeypot token may allow users to purchase tokens while making selling difficult or impossible under the contract’s rules.
A technical investigation can examine the contract’s publicly available code, transaction behavior, and trading activity.
However, a failed sale alone is not automatically proof of fraud. Contract behavior, liquidity, trading restrictions, fees, permissions, and other factors need to be considered.
6. Fake Staking Contracts
A fraudulent staking website may present itself as a legitimate decentralized finance protocol while directing users toward malicious contracts or addresses.
A smart contract fraud investigation can examine the transactions associated with the staking interaction and determine what happened to deposited assets.
How Smart Contract Fraud Differs From a Traditional Crypto Scam
A traditional cryptocurrency scam may simply instruct a victim to send funds to an address.
Smart contract fraud can be more complicated.
The victim may interact with a website and sign a blockchain transaction believing that they are:
- Claiming an airdrop
- Swapping tokens
- Minting an NFT
- Buying a token
- Participating in a presale
- Staking assets
- Connecting to a decentralized application
The transaction may instead grant an unwanted approval or authorize another action.
This means the smart contract fraud investigation must examine the transaction itself rather than relying solely on the victim’s description of what the website promised.
Why Token Approvals Matter
Token approvals are an important component of many decentralized applications.
For example, a user interacting with a decentralized exchange may authorize a contract to spend a specified amount of tokens.
Revoke.cash explains that approvals are stored by token contracts and determine which spender can move tokens on behalf of a wallet.
The security problem arises when a user grants an approval to an untrusted or malicious spender.
Ethereum’s security documentation recommends reviewing and revoking unnecessary permissions and warns about unlimited token allowances.
Therefore, a smart contract fraud investigation may begin by identifying exactly what permission was granted.
What Happens After a Malicious Approval?
Consider a simplified example:
Victim Wallet → Approval Transaction → Malicious Spender → Token Transfer → Secondary Wallet → Additional Wallet
The initial approval may not itself transfer the victim’s tokens.
Instead, the approval gives the authorized spender permission to move certain tokens.
A subsequent transaction may then use that permission.
Chainalysis describes this distinction as an important characteristic of approval-phishing investigations.
This is why examining only the first transaction may provide an incomplete picture.
A complete smart contract fraud investigation can connect the approval transaction with subsequent token transfers.
Smart Contract Code Analysis
Where source code is available and verified, investigators can examine the contract’s programmed functionality.
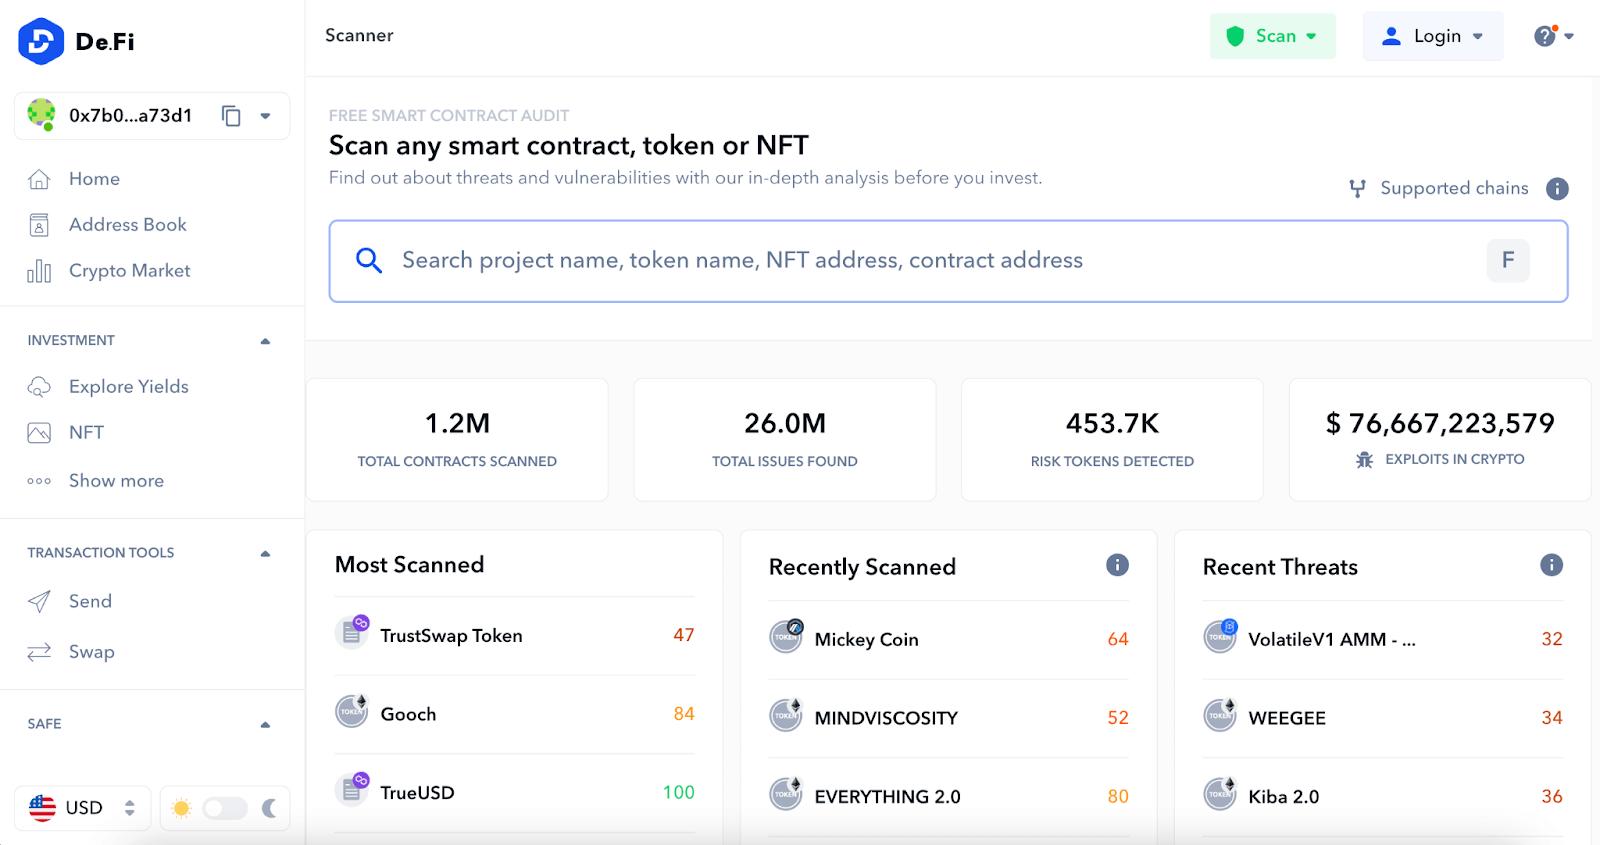
Etherscan provides tools for accessing verified contract source code where developers have published it.
Contract analysis may examine:
- Ownership functions
- Transfer restrictions
- Token approval mechanisms
- Administrative permissions
- Minting functions
- Blacklist mechanisms
- Trading restrictions
- Fee mechanisms
- Withdrawal functions
- Upgrade mechanisms
- External contract interactions
However, verified source code is not always available.
A contract may be unverified, partially verified, proxied, upgraded, or otherwise difficult to interpret.
Therefore, a smart contract fraud investigation should not automatically assume that an unverified contract is fraudulent or that a verified contract is safe.
Code analysis is one component of the broader investigation.
Smart Contract Fraud Investigation for Ethereum
Ethereum is one of the major environments for smart contracts and token activity.
An Ethereum investigation can involve:
- ETH transfers
- ERC-20 tokens
- NFT transactions
- Contract interactions
- Token approvals
- Decentralized exchanges
- DeFi protocols
- Wallet activity
- Contract events
Ethereum’s official documentation provides technical information about transactions and smart-contract interactions.
A smart contract fraud investigation can combine these on-chain records with the victim’s supporting evidence to reconstruct what happened.
Multi-Chain Smart Contract Fraud Investigation
Smart contract incidents are not limited to Ethereum.
Depending on the case, investigation may involve:
- Ethereum
- BNB Chain
- Polygon
- Avalanche
- Arbitrum
- Optimism
- Base
- Solana
- Other supported networks
The exact investigation scope depends on the blockchain involved and the available data.
Different networks use different transaction structures, token standards, explorers, and smart-contract systems.
Therefore, identifying the correct blockchain is an important first step.
How We Analyze a Smart Contract Fraud Case
Step 1: Initial Case Assessment
We review the information you provide and determine whether a smart contract fraud investigation is appropriate.
Useful information may include:
- Contract address
- Wallet address
- Transaction hash
- Blockchain network
- Website URL
- Token name
- Token contract
- Screenshots
- Communication with the project
- Approximate loss
- Date of incident
You do not need to provide your private key or recovery phrase.
Step 2: $99 Case Evaluation
The $99 evaluation establishes the initial scope of the investigation.
We can assess:
- Transaction complexity
- Contract activity
- Wallet movements
- Potential tracing opportunities
- Number of networks involved
- Potential destination services
The evaluation does not guarantee that cryptocurrency can be recovered.
Step 3: Smart Contract Analysis
Where relevant source code or transaction data is available, we examine the contract’s observable behavior.
The objective is to determine what the contract was designed or configured to do and how it interacted with the victim’s wallet.
Step 4: Transaction Reconstruction
Relevant transactions are placed into chronological order.
This may show:
Approval → Unauthorized Transfer → Secondary Wallet → Consolidation → Potential Service Deposit
Step 5: Fund Tracing
The investigation follows the relevant cryptocurrency movements through subsequent addresses where the blockchain data permits.
Our Blockchain Forensic Investigation service can be used when a broader transaction-analysis report is required.
Step 6: Destination Analysis
If funds reach an address associated with a known service, that destination can be documented as an investigative lead.
The blockchain itself does not automatically reveal private customer information held by centralized exchanges.
Step 7: Investigation Report
Findings can be organized into a structured report showing relevant transactions, addresses, timelines, and investigative observations.
What Information Do We Need?
The most useful information for a smart contract fraud investigation generally includes public blockchain information.
Contract Address
The smart contract you interacted with.
Transaction Hash
The transaction associated with your interaction.
Wallet Address
The wallet involved in the transaction.
Blockchain Network
For example:
- Ethereum
- BNB Chain
- Polygon
- Arbitrum
- Base
- Avalanche
- Solana
Website or dApp
The website or decentralized application where you interacted with the contract.
Screenshots
Screenshots can help establish what the victim was shown at the time.
Communications
Emails, Telegram messages, Discord messages, social-media conversations, or other relevant communications can provide additional context.
Our case evaluation page can be used to submit the available information.
Do Not Send Your Private Keys
A legitimate transaction investigation should not require your seed phrase or private key.
These credentials can provide control over cryptocurrency and should remain confidential.
If someone claiming to be a recovery specialist asks you to send your seed phrase so they can “recover” your cryptocurrency, treat the request with extreme caution.
Ethereum’s scam guidance specifically warns users about recovery scams and emphasizes that blockchain transactions cannot simply be reversed.
Our Privacy Policy provides information about privacy practices, while our Terms & Conditions explain applicable service terms.
What If You Approved a Malicious Contract but Your Funds Are Still There?
This situation can require immediate attention.
If you suspect that you granted a malicious token approval, review the approvals associated with the wallet.
Ethereum’s official guidance recommends revoking unwanted token access, while Revoke.cash provides tools for inspecting and revoking token approvals.
Revoke.cash: https://revoke.cash/
Do not assume that disconnecting your wallet from a website automatically removes previously granted token permissions. Ethereum’s documentation specifically distinguishes disconnecting from a dApp from revoking token access.
If you believe the wallet itself has been compromised, consider moving remaining assets to a secure wallet and securing connected accounts, subject to the specifics of your situation.
Can a Smart Contract Fraud Investigation Recover Stolen Crypto?
A smart contract fraud investigation can trace and document cryptocurrency movements, but tracing is not the same as recovery.
This distinction is extremely important.
A confirmed blockchain transaction generally cannot simply be reversed by an investigator.
Ethereum’s official scam guidance states that no one can reverse blockchain transactions.
However, tracing can potentially identify where assets moved and may provide information that can support further action.
For example, a tracing investigation might identify:
Victim Wallet → Malicious Contract → Attacker Wallet → Secondary Wallet → Exchange-Associated Address
If stolen assets reach a centralized service, the identification of that destination may provide a useful lead for legal or law-enforcement processes.
Recent industry investigations have demonstrated that cooperation between blockchain analytics providers, law enforcement, and private-sector platforms can sometimes result in suspected scam proceeds being frozen. For example, Chainalysis reported in April 2026 that an operation involving law-enforcement and private-sector partners secured and froze more than $12 million in suspected criminal proceeds.
That does not mean an individual investigation will result in a freeze or recovery.
Every case depends on the circumstances, timing, jurisdiction, destination of the assets, and cooperation of relevant parties.
Smart Contract Fraud Investigation and Exchange Tracing
Exchange tracing can become important when stolen cryptocurrency reaches a centralized platform.
A blockchain investigation may identify a destination address associated with a known service.
That information can potentially be documented for further investigation.
For example, major cryptocurrency platforms include:
- Binance
- Coinbase
- Kraken
- OKX
- Bybit
- Crypto.com
- Gemini
- KuCoin
- Gate
- Bitstamp
Identification of an exchange-associated address does not automatically identify the customer controlling the account.
Private customer information is generally outside the information available from the public blockchain.
For a broader investigation, our crypto asset tracing service may also be relevant.
Smart Contract Fraud Investigation for Fake Presales
Fake presales can create a particularly useful forensic trail.
A project may advertise:
- Limited token supply
- Early investor bonuses
- Guaranteed allocations
- Exclusive access
- High expected returns
- Countdown timers
- Influencer endorsements
Victims may then be directed to send cryptocurrency to a contract.
A smart contract fraud investigation can examine:
- The presale contract
- The victim’s transaction
- Contract balance and transfers
- Token-distribution activity
- Related wallets
- Subsequent fund movements
- Potential service destinations
If no corresponding token-distribution mechanism exists, that may be a significant investigative observation.
It should still be evaluated alongside the complete contract and transaction history.
Smart Contract Fraud Investigation for Honeypots
Honeypot investigations require careful technical analysis.
A token may appear tradeable but include restrictions affecting selling.
Possible issues can include:
- Trading restrictions
- High transaction fees
- Blacklisting
- Whitelisting
- Maximum transaction limits
- Maximum wallet limits
- Contract-controlled transfer logic
- Liquidity problems
A smart contract fraud investigation can examine the observable contract behavior and transaction history.
The purpose is to distinguish technical limitations from deliberate fraudulent design where the evidence supports such a conclusion.
Smart Contract Fraud Investigation for Wallet Drainers
Wallet-drainer incidents can involve a sequence of permissions and transfers.
For example:
Victim visits website
↓
Victim connects wallet
↓
Victim signs approval
↓
Malicious spender receives permission
↓
Tokens are transferred
↓
Funds move through additional wallets
A smart contract fraud investigation can reconstruct that sequence using the relevant blockchain data.
Chainalysis has documented approval-phishing patterns in which the approved spender address later initiates transfers from the victim’s wallet.
For wallet-drainer cases, our wallet drainer recovery service can be reviewed alongside the forensic investigation.
Evidence Preservation After Smart Contract Fraud
If you believe you have been affected by smart contract fraud, preserve evidence as quickly as possible.
Save:
- Transaction hashes
- Wallet addresses
- Contract addresses
- Website URLs
- Screenshots
- Emails
- Telegram messages
- Discord conversations
- Social-media posts
- Token information
- Exchange records
- Payment records
Ethereum’s scam guidance also recommends documenting transaction hashes, wallet addresses, screenshots, and communications when reporting scams.
Do not delete potentially relevant communications.
You can also review our Disclaimer before submitting your case.
How Long Does a Smart Contract Fraud Investigation Take?
The timeline depends on the complexity of the case.
A relatively straightforward case involving one blockchain and a small number of transactions may require less analysis than a case involving:
- Multiple wallets
- Multiple blockchains
- Bridges
- Token swaps
- DeFi protocols
- Large transaction volumes
- Complex contract interactions
- Multiple suspected entities
The $99 case evaluation is designed to establish the initial scope before a larger investigation is undertaken.
For more information about the process, visit our Case Consultation page.
Why Choose Our Smart Contract Fraud Investigation Service?
Smart Contract Analysis
We examine relevant contract and transaction information to understand the mechanism involved.
Blockchain Transaction Tracing
We reconstruct relevant cryptocurrency movements using available on-chain information.
Evidence-Based Reporting
The investigation focuses on documented transactions and observable blockchain activity.
Multi-Chain Investigation
Cases involving supported blockchain networks can be evaluated based on their actual transaction structure.
No Private Keys Required
Public blockchain information is the starting point for transaction analysis.
Clear Case Evaluation
The $99 evaluation provides an initial assessment before a larger investigation is considered.
You can also review our About Us page for additional information about the company.
How to Reduce Your Risk of Smart Contract Fraud
Prevention is important because blockchain transactions can be difficult or impossible to reverse.
Verify the Website
Check the official project website and avoid links received through unsolicited messages.
Verify the Contract
Where possible, compare the contract address with information published by the project’s official channels.
Review Transaction Permissions
Do not blindly approve unlimited token allowances.
Use a Separate Wallet
A separate wallet can reduce the amount of assets exposed when experimenting with unfamiliar applications.
Revoke Unnecessary Approvals
Review old permissions regularly.
Revoke.cash provides a tool for inspecting and revoking token approvals across supported networks.
Be Careful With Airdrops
Unexpected tokens or NFTs can be used as bait for malicious websites.
Treat Guaranteed Returns With Suspicion
Promises of guaranteed profits, instant rewards, or risk-free cryptocurrency returns are major warning signs.
Do Not Blindly Sign Transactions
The Ethereum Foundation’s 2026 Clear Signing initiative highlights the security risks associated with users approving transactions they cannot meaningfully understand.
Frequently Asked Questions
What is a smart contract fraud investigation?
A smart contract fraud investigation analyzes suspicious smart contracts, transaction activity, token approvals, wallet movements, and related blockchain evidence to understand how a suspected fraud occurred.
Can you analyze a malicious smart contract?
Where sufficient contract and blockchain data is available, we can analyze the observable contract behavior and related transactions.
Can you trace stolen cryptocurrency?
We can analyze blockchain transactions and trace relevant fund movements where the blockchain data permits.
Tracing does not guarantee recovery.
Can a blockchain transaction be reversed?
Generally, confirmed blockchain transactions cannot simply be reversed by an investigator. Ethereum’s official scam guidance explicitly warns users that blockchain transactions cannot be reversed.
Can you recover funds stolen through approval phishing?
A smart contract fraud investigation can identify the approval and subsequent transactions and may provide useful tracing evidence.
Recovery depends on the circumstances and does not have a guaranteed outcome.
What is approval phishing?
Approval phishing is a scam in which a victim is tricked into granting a malicious address or contract permission to spend tokens from their wallet.
What is a drainer contract?
A drainer-related scheme uses malicious transactions, approvals, or contract interactions to facilitate unauthorized asset transfers.
What is a honeypot?
A honeypot token or contract may be designed or configured so that users can acquire an asset but face restrictions when attempting to sell or transfer it.
The exact mechanism requires technical examination.
Do I need to send my private key?
No. Never send your private key or seed phrase for a normal blockchain forensic investigation.
What information do you need?
Usually:
- Contract address
- Wallet address
- Transaction hash
- Blockchain network
- Website URL
- Screenshots
- Relevant communications
I approved a malicious contract but haven’t lost funds yet. What should I do?
Review and revoke suspicious approvals as soon as possible. Ethereum’s official security guidance provides instructions for reviewing and revoking token access.
You can also use Revoke.cash to inspect and revoke supported token approvals.
Is the $99 evaluation a guarantee of recovery?
No. It is an initial investigative evaluation.
Is the $99 evaluation refundable?
Refund eligibility is governed by the applicable service terms. Review our Refund Policy before purchasing.
Can you identify the scammer?
Blockchain analysis may identify addresses, transaction patterns, and potential service destinations. It does not automatically reveal the real-world identity of an address owner.
Can you identify an exchange account?
An investigation may identify a destination address associated with an exchange or other service. Private customer information generally requires appropriate cooperation or legal process.
Start Your Smart Contract Fraud Investigation
If you signed a suspicious smart contract, approved an unfamiliar spender, participated in a fake presale, or lost cryptocurrency after interacting with a questionable decentralized application, preserving the blockchain evidence quickly can be important.
A smart contract fraud investigation can examine the contract, transaction, approval, wallet activity, and subsequent fund movements to build a clearer picture of what happened.
Start with the $99 case evaluation and provide the public blockchain information associated with the incident.
You can also Contact Us if you need assistance before submitting your case.
Never provide your seed phrase, private key, exchange password, or wallet recovery credentials.
Top 10 Cryptocurrency Exchange Resources
When a smart contract fraud investigation identifies a potential exchange destination, the official exchange website may provide useful information about its services and security processes.
These are reference resources, not a ranking or endorsement:
- Binance — https://www.binance.com/
- Coinbase — https://www.coinbase.com/
- Kraken — https://www.kraken.com/
- OKX — https://www.okx.com/
- Bybit — https://www.bybit.com/
- Crypto.com — https://crypto.com/
- Gemini — https://www.gemini.com/
- KuCoin — https://www.kucoin.com/
- Gate — https://www.gate.com/
- Bitstamp — https://www.bitstamp.net/
Additional Authority Resources
Ethereum Security Guidance
Ethereum’s official security guidance explains token approvals, malicious contracts, and steps users can take to revoke unwanted access.
Revoke.cash
Revoke.cash provides tools for reviewing and revoking token approvals across supported networks.
Chainalysis Approval-Phishing Research
Chainalysis has published research describing approval phishing and how attackers use malicious approvals to move assets from victims’ wallets. smart contract fraud investigation
Ethereum Scam Guidance smart contract fraud investigation
Ethereum’s official scam guidance recommends preserving transaction hashes, wallet addresses, screenshots, and communications and warns about cryptocurrency recovery scams.
Reviews
There are no reviews yet.